

Synology has declared a critical security vulnerability affecting multiple products and PHP versions in DSM. Remote attackers could execute arbitrary code on susceptible systems. If you run Synology Calendar, Mail Station, or specific PHP versions, you need to check your software version and update now.
What is the PHP2Shell vulnerability?
Synology says the issue stems from two flaws in how PHP manages memory when out-of-memory errors occur. In both cases, request memory may remain in an unpredictable state and be accessed by later requests. An attacker can exploit this to run arbitrary code on your NAS from the network, without needing to log in or interact with a user.
Synology rates this as critical severity (CVSS score 9.8).
Which Synology products are affected?
Synology says Hyper Backup is not affected. The following packages are vulnerable:
- Synology Calendar (all versions below 3.0.4-21435)
- Mail Station (all versions below 30000002.3.19-20333)
- PHP 7.3, PHP 7.4, PHP 8.0, PHP 8.1, PHP 8.2, PHP 8.3, and PHP 8.4
Synology notes that PHP 7.3 has reached end of life and will not receive a fix.
What should you do now?
Start by checking which versions are currently installed on your NAS:
- For Calendar: upgrade to version 3.0.4-21435 or above
- For Mail Station: upgrade to version 30000002.3.19-20333 or above
- For PHP 7.4: upgrade to 7.4.33-0131 (DSM 7.2 or above), 7.4.33-0122 (DSM 7.0–7.1), or 7.4.33-0010 (DSM 6.2)
- For PHP 8.0: upgrade to 8.0.30-0122 (DSM 7.2 or above) or 8.0.30-0104 (DSM 7.0–7.1)
- For PHP 8.1: upgrade to 8.1.34-0120 or above
- For PHP 8.2: upgrade to 8.2.35-0171 or above
- For PHP 8.3: upgrade to 8.3.36-0051 or above
- For PHP 8.4: upgrade to 8.4.27-0051 or above
Synology says the built-in PHP in DSM is not exposed to external attack surfaces, so the practical risk of exploitation is very low. Even so, updates should be applied as soon as possible.
Full details are available in Synology's official security advisory SA-26:14.
Need help checking and updating your systems?
Ryzen eSolutions is an authorised Synology partner in Malaysia. Our engineers can check the versions running on your NAS, apply these critical updates, and make sure your backup and surveillance systems remain secure. Contact us today—or ask us to add this to your managed support plan.
Source: Synology-SA-26:14 PHP2Shell, published by Synology on 22 October 2026.
Products for this job
Hardware and licences are supplied through our sister shop PrinterBullet. Prices are today's.
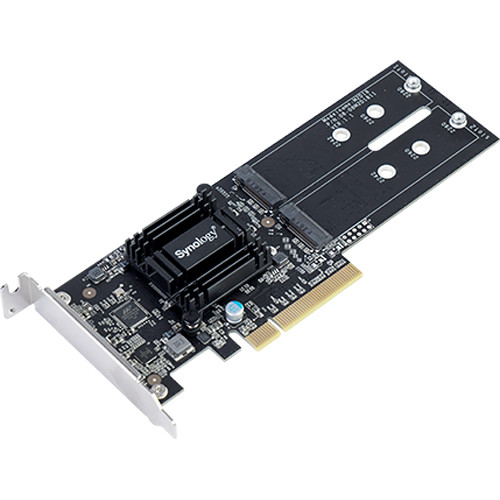 Synology M2D18 Dual M.2 SSD Adapter Card
RM 539.00
 Synology Surveillance Device License Pack 4
RM 1,089.00
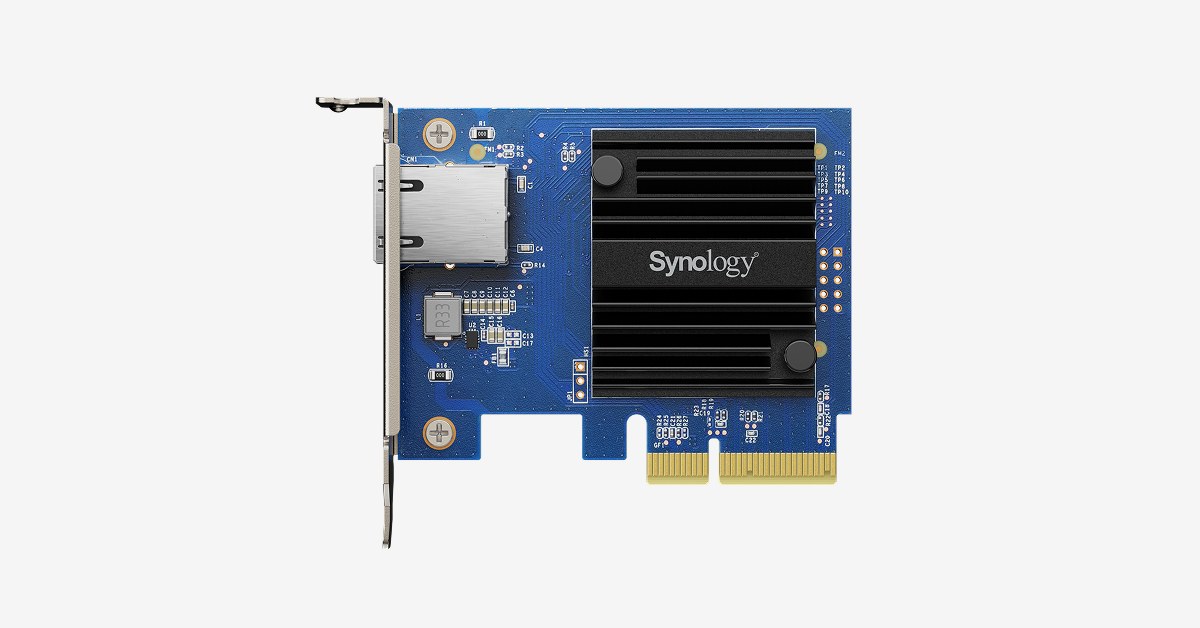 Synology E10G30-T1 Single port 10 Gigabit Base-T PCIe 3.0 x4 Ethernet...
RM 699.00
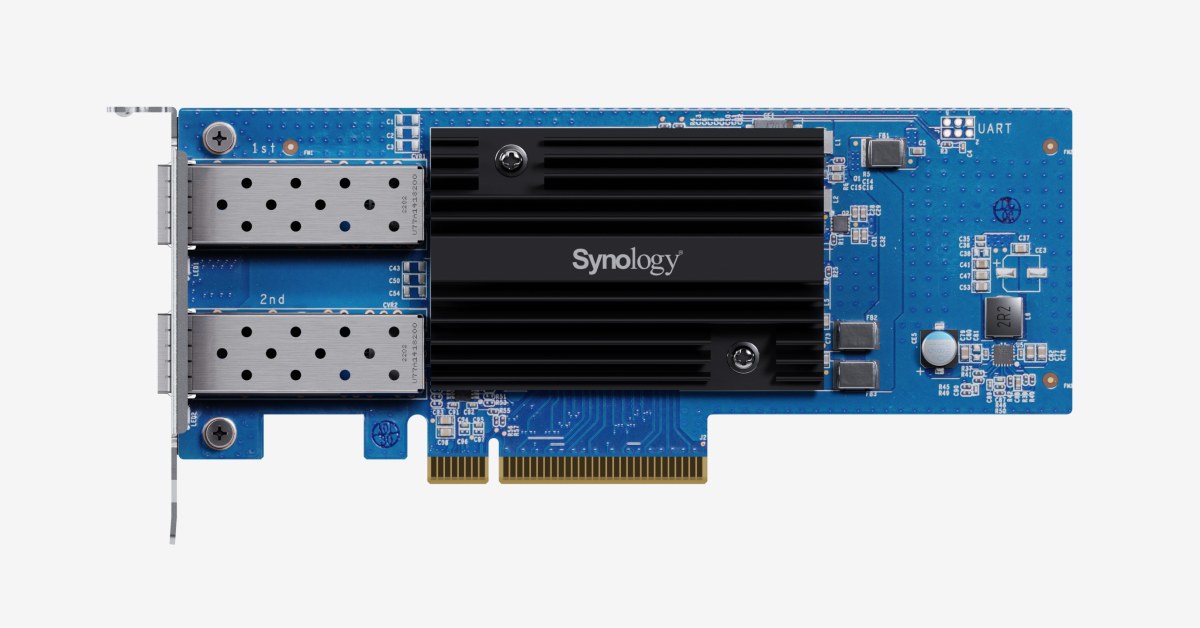 Synology E25G30-F2 dual-port 25GbE SFP28 network card
RM 1,879.00
Frequently asked questions
Is Hyper Backup affected by SA-26:14?
No. Synology says Hyper Backup is not affected by the PHP2Shell vulnerability. Calendar, Mail Station and several PHP versions require updates.
What happens if I don't update?
An attacker on your network could potentially run code on your NAS. Synology notes practical risk is very low because PHP is not exposed externally, but updates should be applied promptly.
How do I check which version of PHP I'm running?
Log into DSM, open Package Centre, find the PHP package, and check the version number. Compare it against the fixed versions listed in this advisory for your DSM release.
Talk this through with an engineer
Free, technical, and specific to your site — that's the consultation.
Book a Consultation