

Synology has announced security updates to address PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619) that affect specific packages running on DiskStation Manager (DSM). If your business runs a Synology NAS with certain web or collaboration tools, you should check whether you need to update. The good news: Synology says the vulnerabilities are limited to systems using particular PHP-dependent applications, and patches are now available across multiple DSM versions.
Which Synology systems and packages are affected?
Synology says the PHP2Shell vulnerabilities only impact systems running these packages: Calendar, IDrive1, Joomla, KodExplorer, MailStation, MediaWiki, phpMyAdmin, vtigerCRM, Web Station, and WordPress. If your NAS does not run any of these applications, your system is not at risk from these particular vulnerabilities.
Note that IDrive (a third-party package) is affected, but Synology Drive is not. If you use Synology Drive for file collaboration and backup, you do not need to take action related to this advisory.
What do I need to do right now?
- If you run any of the affected packages, update PHP immediately through Package Center. Most dependent packages will restart automatically once the update completes.
- MailStation requires a manual restart through Package Center after the PHP update.
- If your system runs DSM 6.2 or later (DSM 6.2, DSM 7.0, DSM 7.1, DSM 7.2, DSM 7.3, or DSM 7.4), security patches are now available for you.
- If you run DSM earlier than version 6.2, Synology recommends disabling the affected packages as a temporary measure and planning an upgrade to a supported DSM version.
Do I need to update the core DSM system?
Synology says the DSM system itself contains a PHP component for internal use only. This component has no external access points and therefore carries minimal risk. Synology plans to patch this component in a future DSM release to maintain compliance, but this is not an urgent security matter.
The critical action is updating PHP through Package Center for the affected applications listed above.
What this means for your business
For most Malaysian businesses running standard NAS or Synology surveillance systems, this update is straightforward. If you host websites, collaboration portals, or other web applications on your NAS, act now. If you use your Synology purely for file storage, backup, or video surveillance, the risk is minimal.
Keeping your Synology systems patched is part of responsible IT housekeeping. Regular updates protect your data and maintain the integrity of your backup and surveillance infrastructure.
If you are unsure whether your Synology NAS runs any of the affected packages, or if you need help applying these updates across multiple sites, Ryzen eSolutions can help. As a Synology authorised partner, we manage and support Synology systems for Malaysian businesses. Contact us to discuss your Synology security posture, or visit our Synology partnership page to learn more about what we offer.
For complete technical details, see the official Synology announcement and Synology-SA-26:14 security advisory.
Source: Synology Statement on PHP2Shell Vulnerabilities, published by Synology on 22 October 2026.
Products for this job
Hardware and licences are supplied through our sister shop PrinterBullet. Prices are today's.
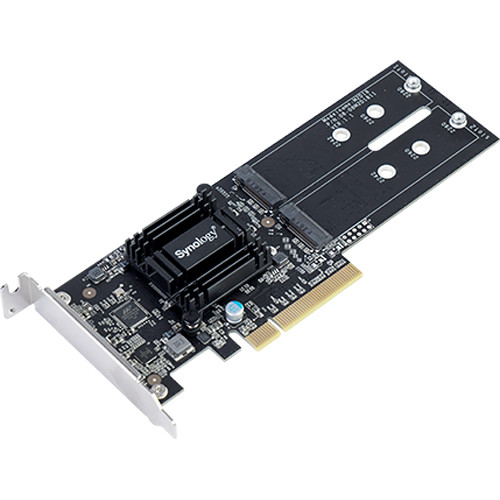 Synology M2D18 Dual M.2 SSD Adapter Card
RM 539.00
 Synology Surveillance Device License Pack 4
RM 1,089.00
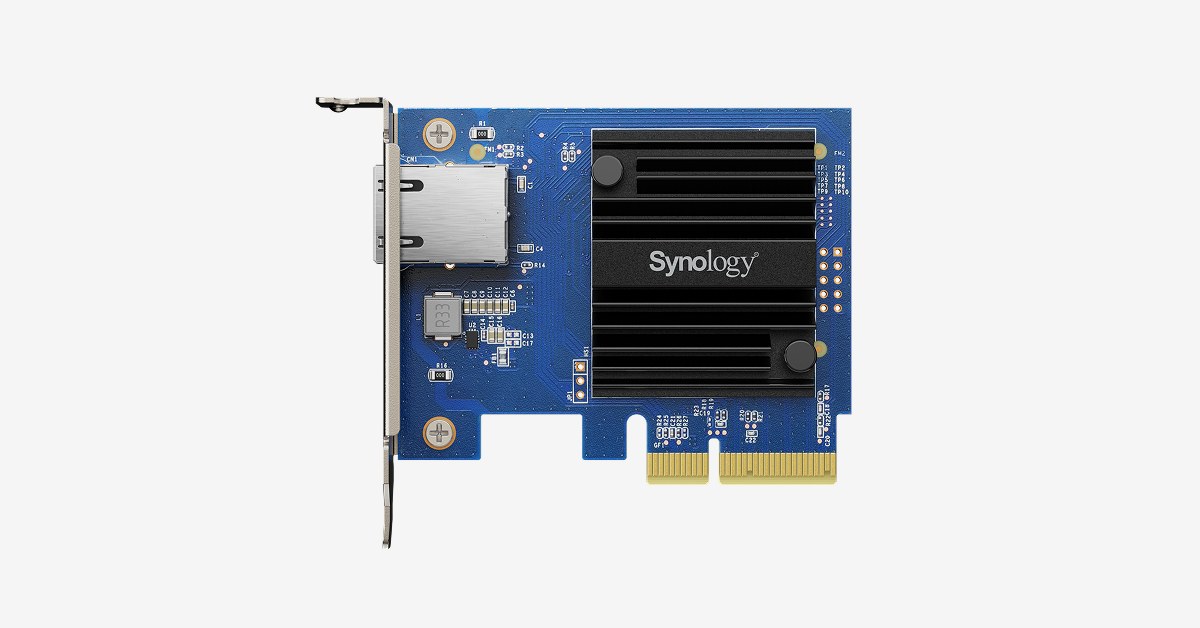 Synology E10G30-T1 Single port 10 Gigabit Base-T PCIe 3.0 x4 Ethernet...
RM 699.00
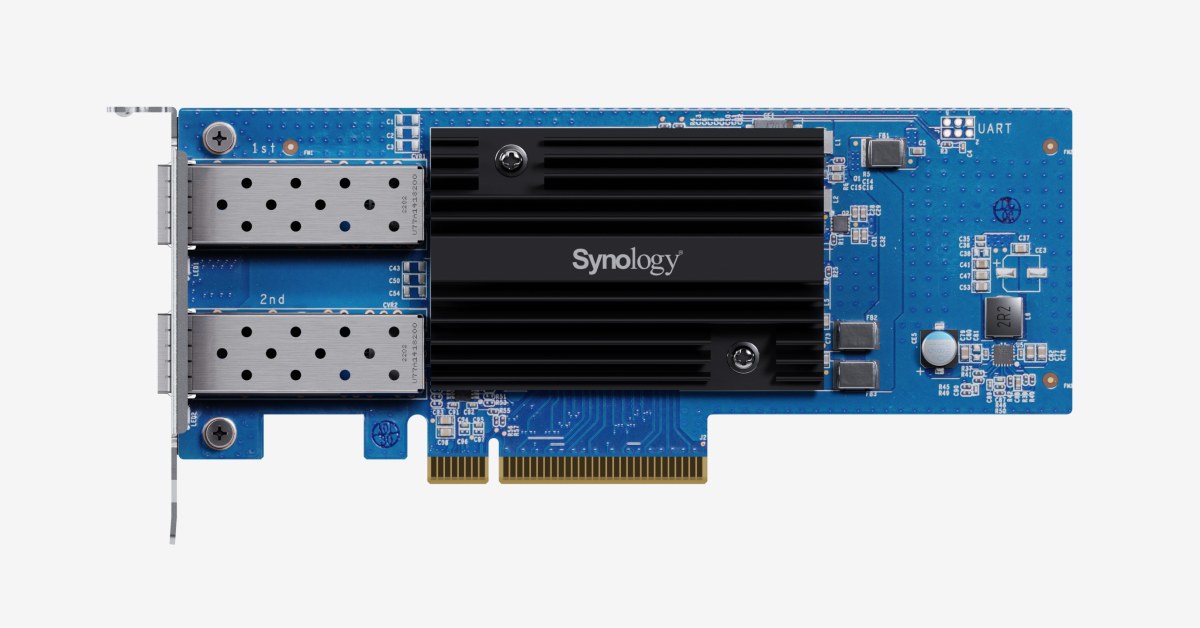 Synology E25G30-F2 dual-port 25GbE SFP28 network card
RM 1,879.00
Frequently asked questions
Do I need to update if I only use my Synology NAS for backup and file storage?
No. The PHP2Shell vulnerabilities only affect systems running specific web and collaboration packages. If you use your NAS purely for backup or storage, you are not at risk from these vulnerabilities.
What happens if I do not update the affected packages?
If you run Calendar, WordPress, phpMyAdmin, or any other affected package, the vulnerabilities could potentially be exploited. Synology strongly recommends updating PHP immediately through Package Center to close the gap.
Can Ryzen help me check and update my Synology systems?
Yes. Ryzen eSolutions is a Synology authorised partner offering installation, configuration, and managed support for Synology NAS and surveillance systems. Contact us to arrange a security check and updates across your systems.
Talk this through with an engineer
Free, technical, and specific to your site — that's the consultation.
Book a Consultation